Most CMMC guidance is written about software, policy documents and managed IT. A real share of the framework lands on the building. Physical protection, media protection, and system and communications protection controls all reach down to cabling, telecom rooms, door hardware and camera coverage. A Space Coast subcontractor can hold a binder of clean policies and still lose the conversation the moment an assessor is standing in front of an unlocked wiring closet.
The obligation runs down the subcontractor tier, not just to the primes
CMMC applies to DoD contractors and subcontractors that process, store or transmit Federal Contract Information or Controlled Unclassified Information under a DoD contract. Company size is not the test. Data is. A twelve-person machine shop in Palm Bay that receives a drawing package marked CUI carries an obligation for that data the same way the Melbourne prime that sent it does.
Brevard County has an unusual concentration of exactly those companies. Aerospace suppliers, test and calibration labs, composite and metal fabricators, engineering firms, and integrators are scattered from Titusville down through Rockledge, Viera, Melbourne and Palm Bay, plus everything feeding launch and payload work on Merritt Island and Cape Canaveral. Many of them learned about CMMC from a flow-down clause rather than from a sales pitch, and most of the follow-up conversation went straight to endpoints, email and policy templates.
The physical layer usually goes unexamined until an assessment is scheduled. That is the wrong order.
The frameworkThree levels, and what each one asks of your facility
CMMC operates under the Version 2.0 final rule framework and is codified into federal acquisition requirements. Which level applies depends on the data you handle and on the program, and cadence differs by level.
| Level | Who it applies to | Controls | Assessment cadence | Infrastructure implications |
|---|---|---|---|---|
| Level 1 — Foundational | Organizations handling Federal Contract Information (FCI) only | 15 basic practices | Annual self-assessment with senior official affirmation | Devices and facilities safeguarded from unauthorized physical access. Locked equipment spaces, controlled visitor access, no open network gear in shared areas. |
| Level 2 — Advanced | Organizations handling Controlled Unclassified Information (CUI) | All 110 NIST SP 800-171 controls | Annual self-assessment for lower-risk programs; C3PAO certification every three years for prioritized acquisitions | Physical access control with monitoring and audit logs, defined and documented segmentation of CUI systems, encryption in transit, media sanitization, logging and monitoring. |
| Level 3 — Expert | Organizations on the highest-priority programs | Level 2 baseline plus enhanced controls from NIST SP 800-172 | Government-led assessment every three years | Everything at Level 2, held to a tighter standard, with the enclave boundary and its evidence expected to hold up under direct government review. |
Confirm your own required level against your contract language and with your assessor. Nobody should be guessing at this from a blog post, including this one.
The part nobody coversSegmentation is a cabling decision before it is a firewall decision
System and communications protection asks you to separate the systems that handle CUI from everything else. That gets treated as a configuration task. In practice, the configuration is only as trustworthy as the physical plant underneath it.
Consider what happens when an assessor asks a plain question: show me where CUI traverses this building. The answer has to be a path. From this workstation, on this labeled drop, through this pathway, into this patch panel in this locked room, onto these switch ports. If the cable plant was installed in pieces over fifteen years by three different vendors, with no labeling scheme and no as-builts, the honest answer is that nobody knows. That is not a firewall problem, and no MSP can fix it from a console.
An enclave you cannot trace with your hands is an enclave you cannot defend on paper.
Physically separating the pathways and patch fields for the CUI enclave is a design choice rather than a mandate. NIST SP 800-171 asks for segmentation without dictating a cable plant. What physical separation buys is a smaller boundary and an assessment answer that a facilities manager can walk through personally, without translating a switch config. For a smaller Brevard supplier where the CUI work is one department and a handful of drops, that scope reduction is often the cheapest control on the list.
Where it landsFive places the physical layer decides your answer
- 1Separate, documented pathways for the CUI enclave Dedicated conduit, trays, patch fields and switching for enclave drops, labeled distinctly from general business traffic. The boundary stops being an abstraction and becomes something an assessor can point at.
- 2Access control on telecom rooms, server rooms and network closets Badge readers, door position sensors and retained audit logs on every space holding enclave equipment. An unlocked wiring closet in a shared-tenant building undermines every logical control sitting behind it, and the audit log is what turns “the door was locked” into evidence.
- 3Camera coverage of entry points and infrastructure spaces Entrances, loading areas and the doors to equipment rooms, at a resolution that identifies a person rather than a shape, with retention you set deliberately and can state from memory. Footage that aged out last week answers nothing.
- 4Labeled, tested, certified cabling with as-builts Standards-based labeling that matches the drawings, certification results for the installed links, and a port-to-outlet map identifying which drops sit inside the boundary. This is the document set that answers where CUI traverses, and it either exists or it does not.
- 5Media handling that includes the infrastructure itself Media protection covers sanitization before disposal, and the scope is wider than laptops. Decommissioned switches and NVRs hold configuration and footage. Even a labeled patch panel or faceplate leaving the building tells someone how the enclave was laid out. Handle it as media, because that is what it is.
BBTS installs, labels, tests and documents the physical infrastructure that supports these control families. BBTS does not certify anyone as CMMC compliant, is not a C3PAO, and does not perform assessments. Those are separate roles, and anyone offering to sell you compliance along with cabling is describing something that does not exist.
Confirm your contractual obligations against your own contract language, and work with your assessor on scope. Then bring the infrastructure up to what that scope requires. Our deliverable is a plant you can hand someone a drawing of.
Brevard’s building stock is part of the problem
A large share of defense and aerospace supplier space in this county sits in older industrial and flex buildings, much of it repeatedly re-tenanted. Telecom rooms end up shared between suites. Cable gets pulled through existing pathways during a tenant improvement and never documented. Copper from two or three generations of tenants is still terminated in the same rack, and nobody can say which pairs are live.
Florida adds its own problems. Unconditioned closets in summer run hot enough to shorten equipment life, and humidity does the rest. Buildings near the river and on the barrier island deal with salt air. None of that is a compliance control by itself, but equipment that fails early and gets swapped in a hurry is exactly how undocumented changes enter a documented enclave.
BBTS has performed facility cabling and infrastructure work at NASA and Kennedy Space Center and for aerospace contractors in the area. That work sets a baseline for how documentation, access and escorting get handled in a controlled environment, and it is the same discipline that a Level 2 assessment expects of a supplier’s own building.
What to have ready before anyone asks
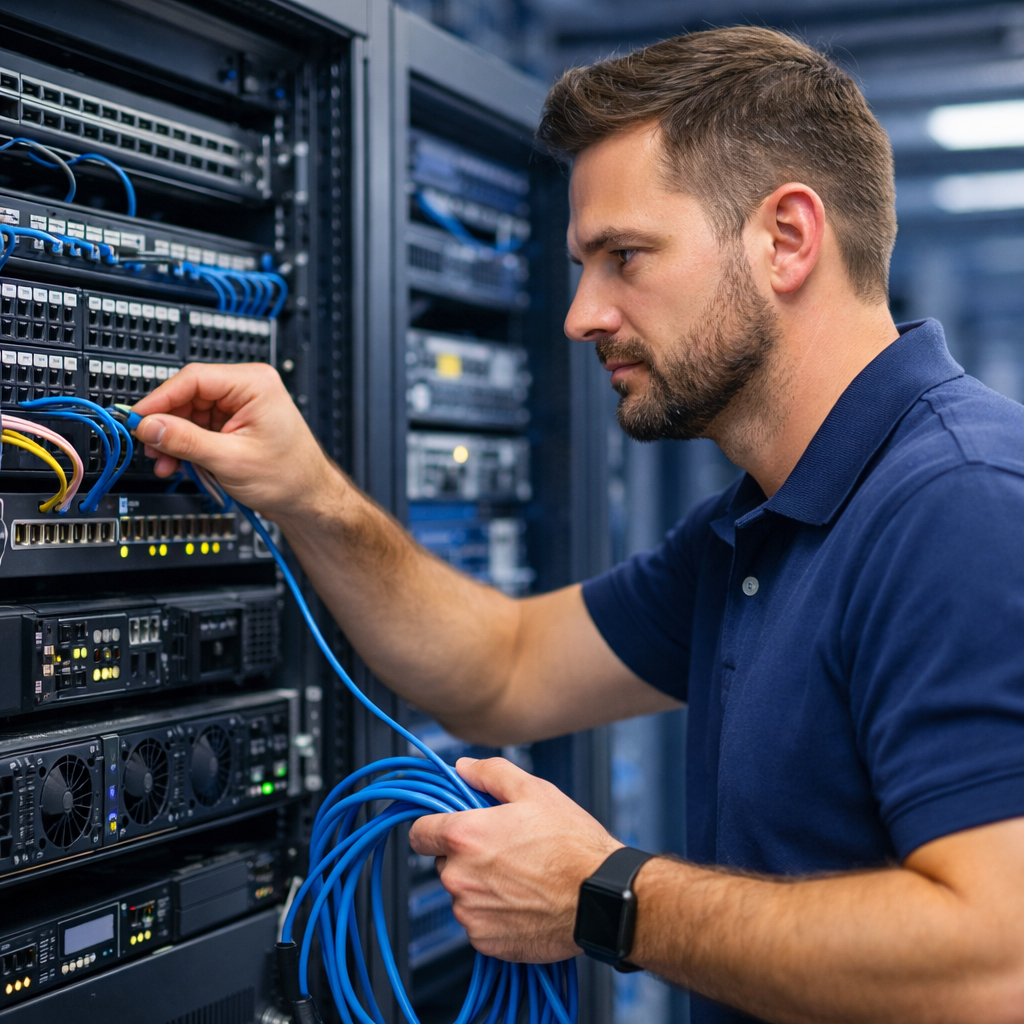
Start with a walk. Open every door that holds network equipment and write down what you find, including who has keys, whether the lock records anything, and whether cameras cover the approach. Pull whatever cabling documentation exists and compare it to the labels physically on the panels. In most buildings that comparison is the fastest way to learn how much of the plant is actually unknown.
From there the work is ordinary. Certify and label what stays, remove what is abandoned, put the enclave on its own documented pathway, secure and monitor the rooms, and set a retention policy you can defend. It is not exotic. It just has to be finished before someone with a checklist shows up, because none of it can be produced on the day of the assessment.
Questions we getFrequently asked questions
Does CMMC apply to us if we are only a subcontractor?
CMMC applies to DoD contractors and subcontractors that process, store or transmit Federal Contract Information or Controlled Unclassified Information under DoD contracts. Tier does not exempt you. A shop in Palm Bay machining parts for a Melbourne prime can carry the same obligation as the prime for the data it actually touches. Read the flow-down clauses in your contract and confirm your required level with your prime and your assessor.
Does new structured cabling make us CMMC compliant?
No. Cabling, access control and surveillance are physical evidence that supports specific control families. Compliance is determined by your assessment, whether that is an annual self-assessment with senior official affirmation or a certification performed by a C3PAO. BBTS installs and documents infrastructure. BBTS does not certify anyone as CMMC compliant, is not a C3PAO and does not perform assessments.
Do we need physically separate cable for CUI, or is a VLAN enough?
NIST SP 800-171 calls for segmentation of the systems that handle CUI. It does not name a specific cable plant design, and logical segmentation is used in plenty of environments. Physical separation of pathways, patch fields and switching is a design decision, not a mandate. What it buys you is a smaller assessment boundary and an answer you can walk an assessor through with your hands. Confirm the approach with whoever is assessing you before you build it.
How long should we retain camera footage covering our server room?
There is no single retention number that applies to every defense contractor. Retention is driven by your own documented policy and by anything your contract specifies. The practical test is whether your retention window is long enough to review an incident you did not notice the same week, and whether you can state the number without checking. Set it deliberately, write it down, then size storage to match.
What cabling documentation should we have on hand before an assessment?
As-built drawings showing pathways and room locations, a labeling scheme that matches the labels physically on the patch panels and outlets, test and certification results for the installed links, and a port-to-outlet map that shows which drops sit inside the CUI boundary. If someone asks where CUI traverses, that packet is the answer.
Have the physical layer sorted before the assessment is scheduled
We will walk your building, document what is actually installed, and tell you plainly where the infrastructure stands. Serving Melbourne, Palm Bay, Titusville, Rockledge, Viera, Merritt Island and Cape Canaveral.